| 文件扩展名 | Content-Type(Mime-Type) | 文件扩展名 | Content-Type(Mime-Type) |
|---|---|---|---|
| .*( 二进制流,不知道下载文件类型) | application/octet-stream | .tif | image/tiff |
| .001 | application/x-001 | .301 | application/x-301 |
| .323 | text/h323 | .906 | application/x-906 |
| .907 | drawing/907 | .a11 | application/x-a11 |
| .acp | audio/x-mei-aac | .ai | application/postscript |
| .aif | audio/aiff | .aifc | audio/aiff |
| .aiff | audio/aiff | .anv | application/x-anv |
| .asa | text/asa | .asf | video/x-ms-asf |
| .asp | text/asp | .asx | video/x-ms-asf |
| .au | audio/basic | .avi | video/avi |
| .awf | application/vnd.adobe.workflow | .biz | text/xml |
| .bmp | application/x-bmp | .bot | application/x-bot |
| .c4t | application/x-c4t | .c90 | application/x-c90 |
| .cal | application/x-cals | .cat | application/vnd.ms-pki.seccat |
| .cdf | application/x-netcdf | .cdr | application/x-cdr |
| .cel | application/x-cel | .cer | application/x-x509-ca-cert |
| .cg4 | application/x-g4 | .cgm | application/x-cgm |
| .cit | application/x-cit | .class | java/* |
| .cml | text/xml | .cmp | application/x-cmp |
| .cmx | application/x-cmx | .cot | application/x-cot |
| .crl | application/pkix-crl | .crt | application/x-x509-ca-cert |
| .csi | application/x-csi | .css | text/css |
| .cut | application/x-cut | .dbf | application/x-dbf |
| .dbm | application/x-dbm | .dbx | application/x-dbx |
| .dcd | text/xml | .dcx | application/x-dcx |
| .der | application/x-x509-ca-cert | .dgn | application/x-dgn |
| .dib | application/x-dib | .dll | application/x-msdownload |
| .doc | application/msword | .dot | application/msword |
| .drw | application/x-drw | .dtd | text/xml |
| .dwf | Model/vnd.dwf | .dwf | application/x-dwf |
| .dwg | application/x-dwg | .dxb | application/x-dxb |
| .dxf | application/x-dxf | .edn | application/vnd.adobe.edn |
| .emf | application/x-emf | .eml | message/rfc822 |
| .ent | text/xml | .epi | application/x-epi |
| .eps | application/x-ps | .eps | application/postscript |
| .etd | application/x-ebx | .exe | application/x-msdownload |
| .fax | image/fax | .fdf | application/vnd.fdf |
| .fif | application/fractals | .fo | text/xml |
| .frm | application/x-frm | .g4 | application/x-g4 |
| .gbr | application/x-gbr | . | application/x- |
| .gif | image/gif | .gl2 | application/x-gl2 |
| .gp4 | application/x-gp4 | .hgl | application/x-hgl |
| .hmr | application/x-hmr | .hpg | application/x-hpgl |
| .hpl | application/x-hpl | .hqx | application/mac-binhex40 |
| .hrf | application/x-hrf | .hta | application/hta |
| .htc | text/x-component | .htm | text/html |
| .html | text/html | .htt | text/webviewhtml |
| .htx | text/html | .icb | application/x-icb |
| .ico | image/x-icon | .ico | application/x-ico |
| .iff | application/x-iff | .ig4 | application/x-g4 |
| .igs | application/x-igs | .iii | application/x-iphone |
| .img | application/x-img | .ins | application/x-internet-signup |
| .isp | application/x-internet-signup | .IVF | video/x-ivf |
| .java | java/* | .jfif | image/jpeg |
| .jpe | image/jpeg | .jpe | application/x-jpe |
| .jpeg | image/jpeg | .jpg | image/jpeg |
| .jpg | application/x-jpg | .js | application/x-javascript |
| .jsp | text/html | .la1 | audio/x-liquid-file |
| .lar | application/x-laplayer-reg | .latex | application/x-latex |
| .lavs | audio/x-liquid-secure | .lbm | application/x-lbm |
| .lmsff | audio/x-la-lms | .ls | application/x-javascript |
| .ltr | application/x-ltr | .m1v | video/x-mpeg |
| .m2v | video/x-mpeg | .m3u | audio/mpegurl |
| .m4e | video/mpeg4 | .mac | application/x-mac |
| .man | application/x-troff-man | .math | text/xml |
| .mdb | application/msaccess | .mdb | application/x-mdb |
| .mfp | application/x-shockwave-flash | .mht | message/rfc822 |
| .mhtml | message/rfc822 | .mi | application/x-mi |
| .mid | audio/mid | .midi | audio/mid |
| .mil | application/x-mil | .mml | text/xml |
| .mnd | audio/x-musicnet-download | .mns | audio/x-musicnet-stream |
| .mocha | application/x-javascript | .movie | video/x-sgi-movie |
| .mp1 | audio/mp1 | .mp2 | audio/mp2 |
| .mp2v | video/mpeg | .mp3 | audio/mp3 |
| .mp4 | video/mpeg4 | .mpa | video/x-mpg |
| .mpd | application/vnd.ms-project | .mpe | video/x-mpeg |
| .mpeg | video/mpg | .mpg | video/mpg |
| .mpga | audio/rn-mpeg | .mpp | application/vnd.ms-project |
| .mps | video/x-mpeg | .mpt | application/vnd.ms-project |
| .mpv | video/mpg | .mpv2 | video/mpeg |
| .mpw | application/vnd.ms-project | .mpx | application/vnd.ms-project |
| .mtx | text/xml | .mxp | application/x-mmxp |
| .net | image/pnetvue | .nrf | application/x-nrf |
| .nws | message/rfc822 | .odc | text/x-ms-odc |
| .out | application/x-out | .p10 | application/pkcs10 |
| .p12 | application/x-pkcs12 | .p7b | application/x-pkcs7-certificates |
| .p7c | application/pkcs7-mime | .p7m | application/pkcs7-mime |
| .p7r | application/x-pkcs7-certreqresp | .p7s | application/pkcs7-signature |
| .pc5 | application/x-pc5 | .pci | application/x-pci |
| .pcl | application/x-pcl | .pcx | application/x-pcx |
| application/pdf | application/pdf | ||
| .pdx | application/vnd.adobe.pdx | .pfx | application/x-pkcs12 |
| .pgl | application/x-pgl | .pic | application/x-pic |
| .pko | application/vnd.ms-pki.pko | .pl | application/x-perl |
| .plg | text/html | .pls | audio/scpls |
| .plt | application/x-plt | .png | image/png |
| .png | application/x-png | .pot | application/vnd.ms-powerpoint |
| .ppa | application/vnd.ms-powerpoint | .ppm | application/x-ppm |
| .pps | application/vnd.ms-powerpoint | .ppt | application/vnd.ms-powerpoint |
| .ppt | application/x-ppt | .pr | application/x-pr |
| .prf | application/pics-rules | .prn | application/x-prn |
| .prt | application/x-prt | .ps | application/x-ps |
| .ps | application/postscript | .ptn | application/x-ptn |
| .pwz | application/vnd.ms-powerpoint | .r3t | text/vnd.rn-realtext3d |
| .ra | audio/vnd.rn-realaudio | .ram | audio/x-pn-realaudio |
| .ras | application/x-ras | .rat | application/rat-file |
| .rdf | text/xml | .rec | application/vnd.rn-recording |
| .red | application/x-red | .rgb | application/x-rgb |
| .rjs | application/vnd.rn-realsystem-rjs | .rjt | application/vnd.rn-realsystem-rjt |
| .rlc | application/x-rlc | .rle | application/x-rle |
| .rm | application/vnd.rn-realmedia | .rmf | application/vnd.adobe.rmf |
| .rmi | audio/mid | .rmj | application/vnd.rn-realsystem-rmj |
| .rmm | audio/x-pn-realaudio | .rmp | application/vnd.rn-rn_music_package |
| .rms | application/vnd.rn-realmedia-secure | .rmvb | application/vnd.rn-realmedia-vbr |
| .rmx | application/vnd.rn-realsystem-rmx | .rnx | application/vnd.rn-realplayer |
| .rp | image/vnd.rn-realpix | .rpm | audio/x-pn-realaudio-plugin |
| .rsml | application/vnd.rn-rsml | .rt | text/vnd.rn-realtext |
| .rtf | application/msword | .rtf | application/x-rtf |
| .rv | video/vnd.rn-realvideo | .sam | application/x-sam |
| .sat | application/x-sat | .sdp | application/sdp |
| .sdw | application/x-sdw | .sit | application/x-stuffit |
| .slb | application/x-slb | .sld | application/x-sld |
| .slk | drawing/x-slk | .smi | application/smil |
| .smil | application/smil | .smk | application/x-smk |
| .snd | audio/basic | .sol | text/plain |
| .sor | text/plain | .spc | application/x-pkcs7-certificates |
| .spl | application/futuresplash | .spp | text/xml |
| .ssm | application/streamingmedia | .sst | application/vnd.ms-pki.certstore |
| .stl | application/vnd.ms-pki.stl | .stm | text/html |
| .sty | application/x-sty | .svg | text/xml |
| .swf | application/x-shockwave-flash | .tdf | application/x-tdf |
| .tg4 | application/x-tg4 | .tga | application/x-tga |
| .tif | image/tiff | .tif | application/x-tif |
| .tiff | image/tiff | .tld | text/xml |
| .top | drawing/x-top | .torrent | application/x-bittorrent |
| .tsd | text/xml | .txt | text/plain |
| .uin | application/x-icq | .uls | text/iuls |
| .vcf | text/x-vcard | .vda | application/x-vda |
| .vdx | application/vnd.visio | .vml | text/xml |
| .vpg | application/x-vpeg005 | .vsd | application/vnd.visio |
| .vsd | application/x-vsd | .vss | application/vnd.visio |
| .vst | application/vnd.visio | .vst | application/x-vst |
| .vsw | application/vnd.visio | .vsx | application/vnd.visio |
| .vtx | application/vnd.visio | .vxml | text/xml |
| .wav | audio/wav | .wax | audio/x-ms-wax |
| .wb1 | application/x-wb1 | .wb2 | application/x-wb2 |
| .wb3 | application/x-wb3 | .wbmp | image/vnd.wap.wbmp |
| .wiz | application/msword | .wk3 | application/x-wk3 |
| .wk4 | application/x-wk4 | .wkq | application/x-wkq |
| .wks | application/x-wks | .wm | video/x-ms-wm |
| .wma | audio/x-ms-wma | .wmd | application/x-ms-wmd |
| .wmf | application/x-wmf | .wml | text/vnd.wap.wml |
| .wmv | video/x-ms-wmv | .wmx | video/x-ms-wmx |
| .wmz | application/x-ms-wmz | .wp6 | application/x-wp6 |
| .wpd | application/x-wpd | .wpg | application/x-wpg |
| .wpl | application/vnd.ms-wpl | .wq1 | application/x-wq1 |
| .wr1 | application/x-wr1 | .wri | application/x-wri |
| .wrk | application/x-wrk | .ws | application/x-ws |
| .ws2 | application/x-ws | .wsc | text/scriptlet |
| .wsdl | text/xml | .wvx | video/x-ms-wvx |
| .xdp | application/vnd.adobe.xdp | .xdr | text/xml |
| .xfd | application/vnd.adobe.xfd | .xfdf | application/vnd.adobe.xfdf |
| .xhtml | text/html | .xls | application/vnd.ms-excel |
| .xls | application/x-xls | .xlw | application/x-xlw |
| .xml | text/xml | .xpl | audio/scpls |
| .xq | text/xml | .xql | text/xml |
| .xquery | text/xml | .xsd | text/xml |
| .xsl | text/xml | .xslt | text/xml |
| .xwd | application/x-xwd | .x_b | application/x-x_b |
| .sis | application/vnd.symbian.install | .sisx | application/vnd.symbian.install |
| .x_t | application/x-x_t | .ipa | application/vnd.iphone |
| .apk | application/vnd.android.package-archive | .xap | application/x-silverlight-app |
标签: Nginx
HTTP Content-type对照表

Linux Apache Nginx SSL证书安装配置图文教程
下载得到的 www.domain.com.zip 文件,解压获得3个文件夹,分别是Apache、IIS、Nginx 服务器的证书文件,
下面提供了4类服务器证书安装方法的示例:Apache 2.x 证书部署
获取证书
Apache文件夹内获得证书文件 1_root_bundle.crt,2_www.domain.com_cert.crt 和私钥文件 3_www.domain.com.key,
1_root_bundle.crt 文件包括一段证书代码 “—–BEGIN CERTIFICATE—–”和“—–END CERTIFICATE—–”,
2_www.domain.com_cert.crt 文件包括一段证书代码 “—–BEGIN CERTIFICATE—–”和“—–END CERTIFICATE—–”,
3_www.domain.com.key 文件包括一段私钥代码“—–BEGIN RSA PRIVATE KEY—–”和“—–END RSA PRIVATE KEY—–”。证书安装
编辑Apache根目录下 conf/httpd.conf 文件,
找到#LoadModule ssl_module modules/mod_ssl.so和#Include conf/extra/httpd-ssl.conf,去掉前面的#号注释;
编辑Apache根目录下 conf/extra/httpd-ssl.conf 文件,修改如下内容:<VirtualHost www.domain.com:443> DocumentRoot "/var/www/html" ServerName www.domain.com SSLEngine on SSLCertificateFile /usr/local/apache/conf/2_www.domain.com_cert.crt SSLCertificateKeyFile /usr/local/apache/conf/3_www.domain.com.key SSLCertificateChainFile /usr/local/apache/conf/1_root_bundle.crt </VirtualHost>配置完成后,重新启动 Apache 就可以使用
https://www.domain.com来访问了。注:
配置文件参数 说明 SSLEngine on 启用SSL功能 SSLCertificateFile 证书文件 SSLCertificateKeyFile 私钥文件 SSLCertificateChainFile 证书链文件 Nginx 证书部署
获取证书
Nginx文件夹内获得SSL证书文件 1_www.domain.com_bundle.crt 和私钥文件 2_www.domain.com.key,
1_www.domain.com_bundle.crt 文件包括两段证书代码 “—–BEGIN CERTIFICATE—–”和“—–END CERTIFICATE—–”,
2_www.domain.com.key 文件包括一段私钥代码“—–BEGIN RSA PRIVATE KEY—–”和“—–END RSA PRIVATE KEY—–”。证书安装
将域名 www.domain.com 的证书文件1_www.domain.com_bundle.crt 、私钥文件2_www.domain.com.key保存到同一个目录,例如/usr/local/nginx/conf目录下。
更新Nginx根目录下 conf/nginx.conf 文件如下:server { listen 443; server_name www.domain.com; #填写绑定证书的域名 ssl on; ssl_certificate 1_www.domain.com_bundle.crt; ssl_certificate_key 2_www.domain.com.key; ssl_session_timeout 5m; ssl_protocols TLSv1 TLSv1.1 TLSv1.2; #按照这个协议配置 ssl_ciphers ECDHE-RSA-AES128-GCM-SHA256:HIGH:!aNULL:!MD5:!RC4:!DHE;#按照这个套件配置 ssl_prefer_server_ciphers on; location / { root html; #站点目录 index index.html index.htm; } }配置完成后,先用
bin/nginx –t来测试下配置是否有误,正确无误的话,重启nginx。就可以使https://www.domain.com来访问了。注:
配置文件参数 说明 listen 443 SSL访问端口号为443 ssl on 启用SSL功能 ssl_certificate 证书文件 ssl_certificate_key 私钥文件 ssl_protocols 使用的协议 ssl_ciphers 配置加密套件,写法遵循openssl标准 使用全站加密,http自动跳转https(可选)
对于用户不知道网站可以进行https访问的情况下,让服务器自动把http的请求重定向到https。
在服务器这边的话配置的话,可以在页面里加js脚本,也可以在后端程序里写重定向,当然也可以在web服务器来实现跳转。Nginx是支持rewrite的(只要在编译的时候没有去掉pcre)
在http的server里增加rewrite ^(.*) https://$host$1 permanent;
这样就可以实现80进来的请求,重定向为https了。
php-fpm 在 MacOS 中重启 图文教程
查看php-fpm端口是否在被php-fpm使用
sudo lsof -i:9000一般修改 php.ini 文件后经常需要重启php-fpm,杀掉全部进程
sudo killall php-fpm启动php-fpm
sudo php-fpm
解决Nginx的connect() to 127.0.0.1:8080 failed (13: Permission denied) while connect
前篇文章我们写了 Docker 下使用Centos系统镜像安装 uwsgi 运行 Python3 Django ,我们在实际运行 Nginx+uWSGI 搭配时出现
502 Bad Getway,在nginx的error.log错误日志中,我们可以看到如下:connect() to 127.0.0.1:8080 failed (13: Permission denied) while connecting to upstream,
经过一番检查以及google,应该是SeLinux的导致的。执行下面命令即可:
setsebool -P httpd_can_network_connect 1
解决WordPress网站被利用xmlrpc.php文件攻击问题
问题描述
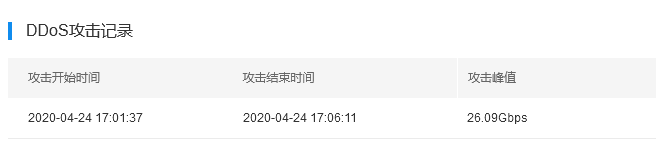
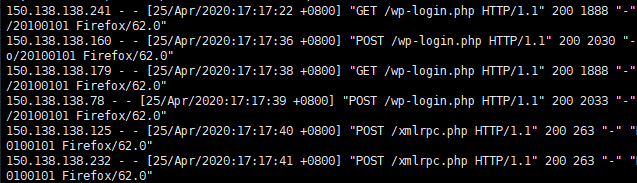
这几天博客经常有出现监控报警VPS宕机的问题,开始我还认为是VPS不稳定造成的(目前用的VPS也有遇到不稳定问题),然后通过日志看到应该是由于有被攻击利用导致的WEB卡死导致的。原因在于使用的WORDPRESS程序默认xmlrpc.php开启,而被用来DDOS攻击导致占用资源过高。

通过日志我们可以看到如下的内容:
解决办法
方法一:利用Nginx直接返回,在对应的主机配置文件中添加
location ~* /xmlrpc.php { deny all; }方法二:屏蔽 XML-RPC (pingback) 的功能
在主题对应的
functions.php中添加如下代码:add_filter('xmlrpc_enabled', '__return_false');方法三:Apache通过.htaccess屏蔽xmlrpc.php文件的访问
# protect xmlrpc <Files xmlrpc.php> Order Deny,Allow Deny from all </Files>Nginx反向代理Google实例
没事研究一下nginx的反向代理,从网上扒了一段,添加 g.laoji.org.conf 配置文件如下:
server { listen 80; server_name g.laoji.org; #你的域名 location / { proxy_pass https://www.google.com/; #需要反代的域名 proxy_redirect off; proxy_set_header X-Real-IP $remote_addr; proxy_set_header X-Forwarded-For $proxy_add_x_forwarded_for; } #add_header X_Via $server_addr; #添加响应头部信息,真实服务器 #add_header X_cache_hit $upstream_cache_status; #添加响应头部信息,是否命中缓存 #sub_filter downloads.wordpress.org downloads.wp.laoji.org; #替换字符串 #sub_filter_last_modified on; #sub_filter_once off; }公司OA项目服务器配置注意点
公司OA项目中需要注意的配置,这里做一下记录。
MySQL部分
在
[mysql]区域下添加配置:innodb_page_size=32k sql-mode=NO_AUTO_CREATE_USER,NO_ENGINE_SUBSTITUTION具体出现问题如下:
- MySQL 倒入数据出现 ERROR 1840 (HY000) at line 24: @@GLOBAL.GTID_PURGED can only be set when @@GLOBAL.GTID_EXECUTED 错误 解决办法
- MySQL调整innodb_page_size之后出现[ERROR] InnoDB: Data file /data/mysql/poweridc/data/ibdata1 is of a different size xxx pages
- MySQL 出现 which is not functionally dependent on columns in GROUP BY clause; this is incompatible with sql_mode=only_full_group_by错误 解决办法 图文教程
- OneinStack PHP 环境添加 calendar 扩展
.sql 文件修改
搜索一下2个部分,将如下部分删除:
- /*!50013 DEFINER=
admin‘@’localhostSQL SECURITY DEFINER */ - /*!50013 DEFINER=
xiaohai@%SQL SECURITY DEFINER */
否则
/xz_sqxg/gong_index将会报错。具体错误请检查 .sql 文件中的视图部分sql代码。
Apache配置
以下配置需写在
.conf文件中,否则不能正常运行。RewriteEngine on RewriteCond %{REQUEST_METHOD} ^TRACE RewriteRule .* - [F] RewriteRule !(^/static|\.(gif|swf|exe|png|jpg|js|css)$) /index.php [L]Nginx
或使用nginx配置
location ~* ^/(?![static])  {
    rewrite ^(.*)$ /index.php last;
}
location ~ \.php$ {
    #root           html;
    fastcgi_pass   jphp-fpm:9000;
    fastcgi_index  index.php;
    fastcgi_param  SCRIPT_FILENAME  /data/wwwroot/POWER_IDC$fastcgi_script_name;
    fastcgi_param  SCRIPT_URL $request_uri;
    include        fastcgi_params;
}
docker logs-查看docker容器日志
前面老季学习了docker的相关知识,在实际的项目中我们知道使用docker logs查看日志,但是如何通过
docker logs命令可以查看容器的指定时间日志,指定最后行数呢?下面我们将会记录一下具体的方法。命令格式
$ docker logs [OPTIONS] CONTAINER
  Options:
        --details        显示更多的信息
    -f, --follow         跟踪实时日志
        --since string   显示自某个timestamp之后的日志,或相对时间,如42m(即42分钟)
        --tail string    从日志末尾显示多少行日志, 默认是all
    -t, --timestamps     显示时间戳
        --until string   显示自某个timestamp之前的日志,或相对时间,如42m(即42分钟)
例子
查看指定时间后的日志,只显示最后100行:
$ docker logs -f -t --since="2018-02-08" --tail=100 CONTAINER_ID查看最近30分钟的日志:
$ docker logs --since 30m CONTAINER_ID查看某时间之后的日志:
$ docker logs -t --since="2018-02-08T13:23:37" CONTAINER_ID查看某时间段日志:
$ docker logs -t --since="2018-02-08T13:23:37" --until "2018-02-09T12:23:37" CONTAINER_IDDocker 本地基本搭建Nginx+PHP-FPM+MARIADB 命令
- 什么是Docker?Docker的架构是什么样的?
- Docker安装Mariadb 设置数据库root密码 图文教程
- Docker 安装 PHP 并配合 Nginx 运行 phpinfo
- Docker 安装 Nginx 映射本地文件 多虚拟主机 图文教程
- Docker中快速删除所有容器
记录一下在MacOS下利用Docker搭建Nginx+php-fpm+MariaDB的常用命令:
# 拉取镜像资源 docker pull mariadb && docker pull bitnami/php-fpm && docker pull nginx # 本地Docoker建立顺序 docker run -d --name jmysql --restart=always -e MYSQL_ROOT_PASSWORD=jjjjjj -e TZ="Asia/Shanghai" mariadb docker run -d --name jphp-fpm -v /wwwroot:/data/wwwroot --restart=always -e TZ="Asia/Shanghai" --link jmysql bitnami/php-fpm docker run -d --name jnginx -v /DockerConfig/nginx/conf.d:/etc/nginx/conf.d -v /wwwroot:/data/wwwroot -p 8081:80 --restart=always -e TZ="Asia/Shanghai" --link jphp-fpm --link jmysql nginx #启动顺序 docker start jmysql docker start jphp-fpm docker start jnginxDocker 安装 PHP 并配合 Nginx 运行 phpinfo
搜索安装 PHP 镜像
docker pull php查找Docker Hub上的php镜像
$
docker search phpNAME DESCRIPTION STARS OFFICIAL AUTOMATED php While designed for web development, the PH... 1232 [OK] richarvey/nginx-php-fpm Container running Nginx + PHP-FPM capable ... 207 [OK] phpmyadmin/phpmyadmin A web interface for MySQL and MariaDB. 123 [OK] eboraas/apache-php PHP5 on Apache (with SSL support), built o... 69 [OK] php-zendserver Zend Server - the integrated PHP applicati... 69 [OK] million12/nginx-php Nginx + PHP-FPM 5.5, 5.6, 7.0 (NG), CentOS... 67 [OK] webdevops/php-nginx Nginx with PHP-FPM 39 [OK] webdevops/php-apache Apache with PHP-FPM (based on webdevops/php) 14 [OK] phpunit/phpunit PHPUnit is a programmer-oriented testing f... 14 [OK] tetraweb/php PHP 5.3, 5.4, 5.5, 5.6, 7.0 for CI and run... 12 [OK] webdevops/php PHP (FPM and CLI) service container 10 [OK] ...这里我们拉取官方的镜像,标签为5.6-fpm
$
docker pull bitnami/php-fpm等待下载完成后,我们就可以在本地镜像列表里查到REPOSITORY为php,标签为5.6-fpm的镜像。
$
docker imagesREPOSITORY TAG IMAGE ID CREATED SIZE bitnami/php-fpm latest 84abb84939ff About an hour ago 246MB php latest f0357c41bff5 10 days ago 367MB nginx latest 719cd2e3ed04 2 weeks ago 109MB docker4w/nsenter-dockerd latest 2f1c802f322f 8 months ago 187kBNginx + PHP 部署
Nginx 部署可以查看:Docker 安装 Nginx,一些 Nginx 的配置参考这篇文章。
启动PHP容器
$
docker run -d --name jphp-fpm -v D:\wwwroot\POWER_IDC:/data/wwwroot/poweridc bitnami/php-fpm命令说明:
- –name
jphp-fpm: 将容器命名为 jphp-fpm。 - -v
D:\wwwroot\POWER_IDC:/data/wwwroot/poweridc将主机中项目的目录 POWER_IDC 挂载到容器的data/wwwroot/poweridc
查看php容器IP
docker inspect --format '{{ .NetworkSettings.IPAddress }}' jphp-fpm配置Nginx的虚拟主机文件
在该目录下修改
D:\DockerConfig\nginx\conf.d\poweridc.conf文件,内容如下:server { listen 80; server_name poweridc; #charset koi8-r; #access_log /var/log/nginx/host.access.log main; location / { root /data/wwwroot/poweridc; index index.html index.htm; } #error_page 404 /404.html; # redirect server error pages to the static page /50x.html # error_page 500 502 503 504 /50x.html; location = /50x.html { root /usr/share/nginx/html; } # proxy the PHP scripts to Apache listening on 127.0.0.1:80 # #location ~ \.php$ { # proxy_pass http://127.0.0.1; #} # pass the PHP scripts to FastCGI server listening on 127.0.0.1:9000 # location ~ \.php$ { #root html; fastcgi_pass jphp-fpm:9000;#下面用了--link参数,hosts里会自动解析ip fastcgi_index index.php; fastcgi_param SCRIPT_FILENAME /data/wwwroot/poweridc/$fastcgi_script_name; include fastcgi_params; } # deny access to .htaccess files, if Apache's document root # concurs with nginx's one # #location ~ /\.ht { # deny all; #} }配置文件说明:
- 172.17.0.3:9000: 表示 php-fpm 服务的容器地址,上面已经说明。
启动Nginx
docker run -d -p 8081:80 --name jnginx -v D:\wwwroot\POWER_IDC:/data/wwwroot/poweridc -v D:\DockerConfig\nginx\conf.d\poweridc.conf:/etc/nginx/conf.d/poweridc.conf -v D:\DockerConfig\nginx\logs:/etc/nginx/logs --link jphp-fpm:bitnami/php-fpm nginx- -p 8081:80: 端口映射,把 nginx 中的 80 映射到本地的 8081 端口。
- D:\wwwroot\POWER_IDC: 是本地 html 文件的存储目录,/data/wwwroot/poweridc 是容器内 html 文件的存储目录。
- D:\DockerConfig\nginx\conf.d\poweridc.conf: 是本地 nginx 配置文件的存储目录,/etc/nginx/conf.d/poweridc.conf 是容器内 nginx 配置文件的存储目录。
运行php文件
接下来我们在 D:\wwwroot\POWER_IDC 目录下创建 info.php,代码如下:
<?php phpinfo();
浏览器打开 http://poweridc:8081/info.php,显示如下:
- –name
Docker 安装 Nginx 映射本地文件 多虚拟主机 图文教程
Docker命令行如何安装Nginx?
docker pull nginx 命令安装
查找 Docker Hub 上的 nginx 镜像
$
docker search nginxNAME DESCRIPTION STARS OFFICIAL AUTOMATED nginx Official build of Nginx. 3260 [OK] jwilder/nginx-proxy Automated Nginx reverse proxy for docker c... 674 [OK] richarvey/nginx-php-fpm Container running Nginx + PHP-FPM capable ... 207 [OK] million12/nginx-php Nginx + PHP-FPM 5.5, 5.6, 7.0 (NG), CentOS... 67 [OK] maxexcloo/nginx-php Docker framework container with Nginx and ... 57 [OK] ...这里我们拉取官方的镜像
$
docker pull nginx等待下载完成后,我们就可以在本地镜像列表里查到 REPOSITORY 为 nginx 的镜像。
$
docker images nginxREPOSITORY TAG IMAGE ID CREATED SIZE nginx latest 555bbd91e13c 3 days ago 182.8 MBDocker中如何启动Nginx实例?
以下命令使用 NGINX 默认的配置来启动一个 Nginx 容器实例:
$
docker run --name jiloc-nginx-test -p 8081:80 -d nginxjiloc-nginx-test容器名称。- the
-d设置容器在在后台一直运行。 - the
-p端口进行映射,将本地 8081 端口映射到容器内部的 80 端口。
执行以上命令会生成一串字符串,类似 0c3b0eaaa36657306e4586cfd613f5e37bbff0423cc3e58ee3683b4a1f1458f5,这个表示容器的 ID,一般可作为日志的文件名。
我们可以使用 docker ps 命令查看容器是否有在运行:
$
docker psCONTAINER ID IMAGE ... PORTS NAMES 0c3b0eaaa366 nginx ... 0.0.0.0:8081->80/tcp jiloc-nginx-testPORTS 部分表示端口映射,本地的 8081 端口映射到容器内部的 80 端口。
在浏览器中打开 http://127.0.0.1:8081/,效果如下:
Docker部署nginx设置配置文件
首先,创建目录 nginx, 用于存放后面的相关东西。
$
mkdir -p ~/nginx/www ~/nginx/logs ~/nginx/conf拷贝容器内 Nginx 默认配置文件到本地当前目录下的 conf 目录,容器 ID 可以查看 docker ps 命令输入中的第一列:
docker cp 0c3b0eaaa366:/etc/nginx/nginx.conf ~/nginx/conf- www: 目录将映射为 nginx 容器配置的虚拟目录。
- logs: 目录将映射为 nginx 容器的日志目录。
- conf: 目录里的配置文件将映射为 nginx 容器的配置文件。
- :ro 只读
部署命令
$
docker run -d -p 8082:80 --name jiloc-nginx-test-web -v ~/nginx/www:/usr/share/nginx/html -v ~/nginx/conf/nginx.conf:/etc/nginx/nginx.conf:ro -v ~/nginx/logs:/var/log/nginx nginx已有源码 Windows 本地映射,启动Docker开启虚拟主机
docker run -d -p 8081:80 --name jnginx -v D:\wwwroot\POWER_IDC:/data/wwwroot/poweridc -v D:\DockerConfig\nginx\conf.d\poweridc.conf:/etc/nginx/conf.d/poweridc.conf nginx命令说明:
- -p 8082:80: 将容器的 80 端口映射到主机的 8082 端口。
- –name jiloc-nginx-test-web:将容器命名为 jiloc-nginx-test-web。
- -v ~/nginx/www:/usr/share/nginx/html:将我们自己创建的 www 目录挂载到容器的 /usr/share/nginx/html。
- -v ~/nginx/conf/nginx.conf:/etc/nginx/nginx.conf:将我们自己创建的 nginx.conf 挂载到容器的 /etc/nginx/nginx.conf。
- -v ~/nginx/logs:/var/log/nginx:将我们自己创建的 logs 挂载到容器的 /var/log/nginx。
启动以上命令后进入 ~/nginx/www 目录:
$
cd ~/nginx/www创建 index.html 文件,内容如下:
<!DOCTYPE html>
<html>
<head>
<meta charset="utf-8">
<title>菜鸟教程(laoji.org)</title>
</head>
<body>
    <h1>我的第一个标题</h1>
    <p>我的第一个段落。</p>
</body>
</html>
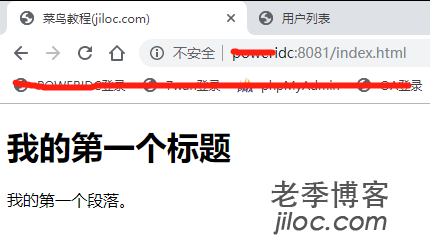
输出结果为:
我们这里使用的是自定义域名,设置方法请看:
Linux Windows MacOS 等系统中hosts的原理及作用
相关命令
如果要重新载入 NGINX 可以使用以下命令发送 HUP 信号到容器:
$
docker kill --signal=SIGHUP container-name重启 NGINX 容器命令:
$
docker restart container-nameNginx常用屏蔽规则,让网站更安全
Nginx (engine x) 是一个高性能的HTTP和反向代理服务,目前很大一部分网站均使用了Nginx作为WEB服务器,Nginx虽然非常强大,但默认情况下并不能阻挡恶意访问,老季整理了一份常用的Nginx屏蔽规则,希望对你有所帮助。
在开始之前,希望您已经熟悉Nginx常用命令(如停止、重启等操作)及排查nginx错误日志,以免出现问题不知所措。如无特殊注明,以下的命令均添加到
server段内,修改nginx配置之前务必做好备份,修改完毕后需要重载一次nginx,否则不会生效。如何防止莫名的文件被下载?
比如将网站数据库导出到站点根目录进行备份,很有可能也会被别人下载,从而导致数据丢失的风险。以下规则可以防止一些常规的文件被下载,可根据实际情况增减。
location ~ \.(zip|rar|sql|bak|gz|7z)$ {
  return 444;
}
屏蔽非常见蜘蛛(爬虫)
如果经常分析网站日志你会发现,一些奇怪的UA总是频繁的来访问网站,而这些UA对网站收录毫无意义,反而增加服务器压力,可以直接将其屏蔽。
if ($http_user_agent ~* (SemrushBot|python|MJ12bot|AhrefsBot|AhrefsBot|hubspot|opensiteexplorer|leiki|webmeup)) {
     return 444;
}
禁止某个目录执行脚本
比如网站上传目录,通常存放的都是静态文件,如果因程序验证不严谨被上传木马程序,导致网站被黑。以下规则请根据自身情况改为您自己的目录,需要禁止的脚本后缀也可以自行添加。
#uploads|templets|data 这些目录禁止执行PHP
location ~* ^/(uploads|templets|data)/.*.(php|php5)$ {
    return 444;
}
屏蔽某个IP或IP段
如果网站被恶意灌水或CC攻击,可从网站日志中分析特征IP,将其IP或IP段进行屏蔽。
#屏蔽192.168.5.23这个IP
deny 192.168.5.23;
#屏蔽192.168.5.* 这个段
denu 192.168.5.0/24;
其它说明
再次强调,修改nginx配置之前务必做好备份,修改完毕后需要重载一次nginx,否则不会生效。
上面大部分规则返回
444状态码而不是403,因为444状态码在nginx中有特殊含义。nginx的444状态是直接由服务器中断连接,不会向客户端再返回任何消息,比返回403更加暴力。若有不足还请补充和指正。